01.
Full attack-chain reconstruction
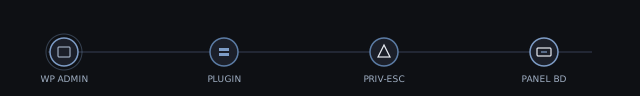
Forensic reconstruction of a WordPress admin compromise that escalated to a reseller-level control-panel backdoor.
Read case studySecurity specialist
Fleet hardening, incident reconstruction, evidence-linked decisions — dense signal, no clutter.
02.
Every number links to evidence on this site.
In progress: PortSwigger Academy · HackerOne path
03.
Problem → Detection → Action → Result. Employer names omitted.
01.
Forensic reconstruction of a WordPress admin compromise that escalated to a reseller-level control-panel backdoor.
Read case study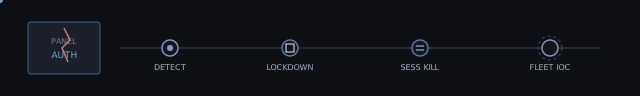
02.
CVSS 9.8-class hosting-panel authentication bypass: lockdown, session kill, service masking, and fleet-wide IoC sweep.
Read case study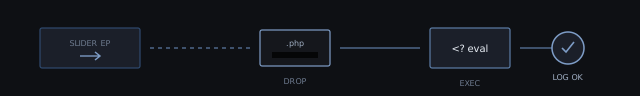
03.
Slider-plugin vulnerability leading to webshell; confirmed and traced via security-monitoring logs.
Read case study04.
Real tooling for fleet and SOC workflows.
CVE watch that polls NVD and RSS, deduplicates findings, and alerts via Telegram/email when CVSS ≥ 9.0 or a fleet-relevance match fires — scheduled with systemd timers.
View on GitHubControl-panel patch awareness: tracks upstream cPanel/WHM advisories and surfaces missing or delayed patches across managed hosts.
View on GitHubResearch tooling and notes around WordPress XML-RPC abuse patterns: amplification, credential stuffing, and practical mitigations.
View on GitHubLightweight WordPress attack detection: log parsing heuristics for brute-force, plugin probe storms, and suspicious admin-ajax / REST patterns.
View on GitHub05.
Real tools and technologies in day-to-day work.
06.
Hand-rolled hardening — verifiable.
06.
For security roles or select consulting — form or direct email.