06.
Critical panel auth-bypass incident response
CVSS 9.8-class hosting-panel authentication bypass: lockdown, session kill, service masking, and fleet-wide IoC sweep.
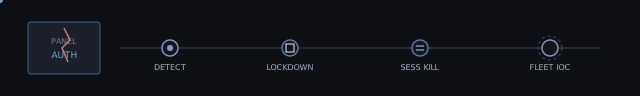
Problem
A critical authentication-bypass class issue (CVSS 9.8 range) affecting the hosting control panel authentication path became actionable. Unauthenticated callers could reach privileged panel API surfaces. Exposure window included production endpoints fronting fleet nodes such as 10.0.0.15–10.0.0.48.
Detection
Vendor advisory plus internal canary traffic confirmed the bypass class. Panel access logs showed unauthenticated privileged method calls from unfamiliar ASN ranges. Session stores listed tokens minted without a preceding successful login event.
Action
Executed IR runbook: put panel listeners behind emergency ACL / service mask, invalidated all active sessions and API tokens, rotated reseller and root panel secrets, applied vendor hotfix, then swept the fleet for IoCs (unexpected admin accounts, modified panel binaries, anomalous cron). Coordinated customer communication without disclosing exploit detail.
Result
Authentication path restored under patched builds. Sweep found no confirmed pre-patch exploitation on this fleet; residual risk closed by session invalidation and secret rotation. Post-incident: continuous advisory watch wired into patch radar tooling.