06.
Full attack-chain reconstruction
Forensic reconstruction of a WordPress admin compromise that escalated to a reseller-level control-panel backdoor.
Problem
A customer WordPress site on a shared hosting node showed persistent reinfection after routine malware cleanup. Initial indicators pointed past a simple webshell: unknown admin users, a freshly uploaded plugin under an innocuous name, and anomalous root-adjacent activity on host [REDACTED_HOST] (example node 10.0.0.42).
Detection
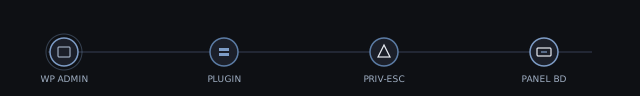
Timeline correlation across access logs, WordPress audit trails, and host telemetry reconstructed the sequence: compromised wp-admin session → malicious plugin drop → local privilege-escalation exploit against an outdated kernel package → installation of a reseller-scoped control-panel backdoor. IoCs included a unique user-agent cluster and outbound callbacks to 10.0.0.88.
Action
Isolated the node from the shared pool, preserved disk and memory artifacts, removed the malicious plugin and backdoor accounts, rotated all panel and SSH credentials for the affected reseller tree, and patched the privilege-escalation path. Parallel hunt across sibling hosts for the same IoC set.
Result
Chain fully mapped with artifact hashes and a reusable playbook for "cleanup that keeps coming back." No lateral reinfection observed after credential rotation and kernel remediation. Findings fed detection rules for plugin-drop + unexpected panel API calls.